E2P // SERVICE CATALOGUEREF ID: L01-QHSC
LEVEL 01NON-INTRUSIVE2-3 days DELIVERY
Quick Web Security Health Check
Targeted surface reconnaissance & entry-level exposure screening.
REGULAR: $50 USD
🎉 FIRST 20 ORGS FREE
// ASSESSMENT OBJECTIVE
Designed for small businesses, startups, and organizations seeking an immediate, lightweight verification of their web application security baseline. Identifies public surface exposures, transport layer misconfigurations, and standard security header omissions without operational downtime.
TECHNICAL SCOPE & ASSESSMENT BREAKDOWN (tap to expand / collapse)
01. Website Availability & HTTPS Baseline
- HTTP to HTTPS automatic redirection validation.
- SSL/TLS certificate expiration & validity chain inspection.
- Basic TLS protocol version support evaluation (TLS 1.2 / 1.3 checks).
02. Security Headers & Cookie Attributes
- Verification of critical HTTP headers:
HSTS,CSP,X-Frame-Options,X-Content-Type-Options. - Cookie security flag enforcement checks (
Secure,HttpOnly,SameSite).
03. Technology & Server Information Disclosure
- Passive server version header leakage identification (e.g., Nginx, Apache, IIS).
- Public web framework fingerprinting (WordPress, React, Laravel, etc.).
04. Common Security Misconfigurations
- Detection of active Directory Listing / Indexing permissions.
- Public accessibility of sensitive files (
robots.txt,.gitexposure, default admin panels).
05. Basic Exposure & Vulnerability Screening
- Screening against known CVE databases for detected public software versions.
- High-level triage of potential perimeter attack surface risks.
📦 Deliverables Provided
A concise, executive-ready 2 to 3-page PDF Security Health Brief containing identified risks, severity rankings (Critical to Info), and clear step-by-step remediation guidance.
🎯 Target Eligibility
Suitable for 1 primary domain or target host (e.g.,
https://example.com). Excludes multi-tenant SaaS environments or massive enterprise subnets.⚠️ Important Limitation Note: Level 01 is an automated, non-intrusive health assessment. It does not include deep manual penetration testing, source code audit, or intrusive exploitation.
// ORDER SERVICE OPTIONS
Scope authorization and domain ownership confirmation are required before scan execution.
📸 Sample Deliverable / Technical Finding Preview
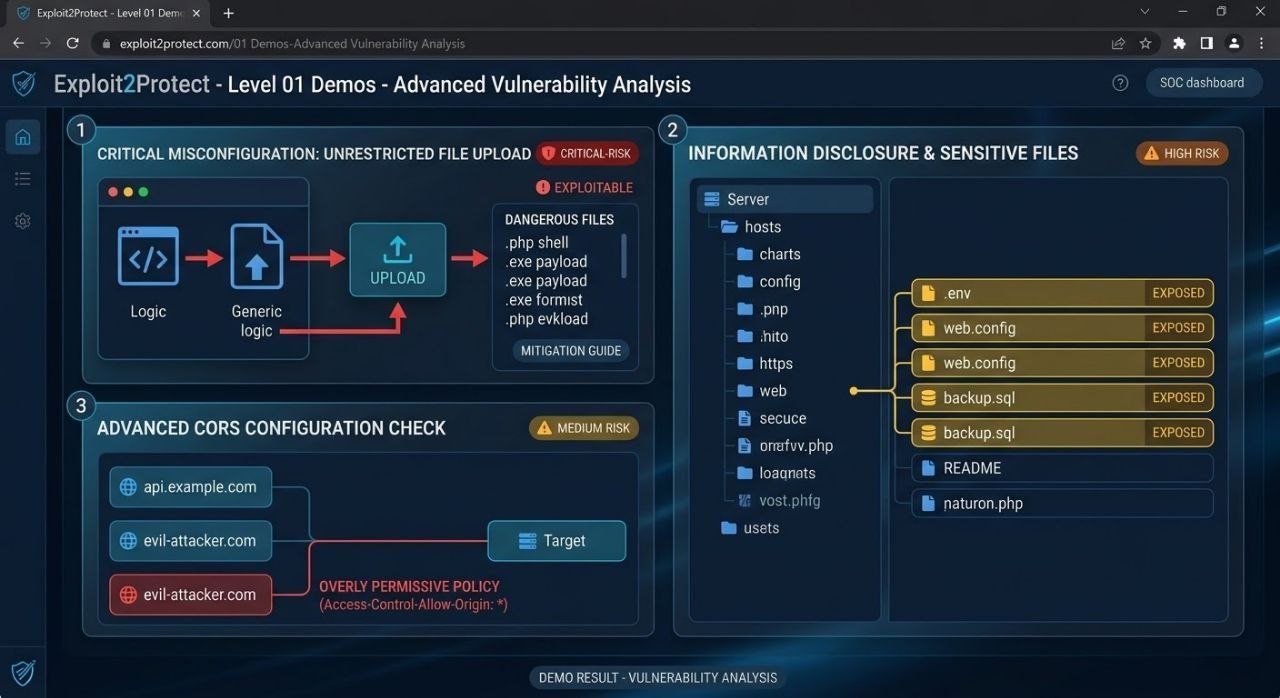
Real-world threat breakdown & clear remediation steps included in every assessment report.
●SYSTEM READY // EXPLOIT2PROTECT SECURITY SERVICESTURNING ATTACKS INTO DEFENSE
E2P // SERVICE CATALOGUEREF ID: L02-WPA
LEVEL 02MANUAL + AUTOMATED5-7 DAYS DELIVERY
Web Pentesting & Assessment
Manual exploit verification, OWASP-based testing & a professional pentest report.
PRICE
$200 USD
// ASSESSMENT OBJECTIVE
Protect your web application against real-world threats. We combine automated testing with manual vulnerability validation to find weaknesses, prove their impact, and give you clear, actionable remediation guidance.
// WHAT'S INCLUDED
🎯
Single Domain Scope
1 domain or web application, agreed boundaries
🛡️
OWASP Top 10
Risk-based, not just scanners
🧪
Manual Exploit Verification
Safe proof of concept, no false positives
📄
Professional Pentest Report
CVSS, CWE, evidence, remediation
🔁
Free Retest
1x within 30 days
// TECHNICAL SCOPE & BREAKDOWN (tap to expand)
A. Single Domain Scope
The assessment covers one domain or web application, for example
https://example.com.- One approved domain / application
- Agreed testing boundaries
- Defined testing period
- Written authorization before testing starts
Note: additional domains, subdomains, APIs, mobile apps and admin portals are not automatically included. Scope is defined and agreed before work begins.
B. OWASP Top 10 Coverage
Tested against the current OWASP Top 10 using a risk-based approach.
| Security area | Example testing |
|---|---|
| Access Control | IDOR, privilege escalation |
| Security Misconfiguration | Exposed debug features, unsafe configuration |
| Software Supply Chain | Vulnerable dependencies and related risks |
| Cryptographic Failures | Weak protection of sensitive data |
| Injection | SQL injection, command injection, XSS |
| Insecure Design | Abuse of business workflows |
| Authentication Failures | Login weaknesses, account takeover paths |
| Integrity Failures | Unsafe trust or integrity controls |
| Logging & Alerting | Important security events not detected |
| Exceptional Conditions | Unsafe error handling |
C. Manual Exploit Verification
Every finding is manually validated, not copied from scanner output. Impact is demonstrated safely with minimal data access.
- IDOR: verify unauthorized access to another test account's resource
- XSS: demonstrate controlled JavaScript execution
- SQL Injection: confirm injection behavior with minimal-impact testing
- Authentication: validate an actual bypass
- Privilege Escalation: demonstrate unauthorized privilege changes
- Business Logic: show a real workflow abuse scenario
D. Professional Pentest Report
A branded PDF report with:
- Executive summary, scope, methodology and testing limitations
- Risk summary and vulnerability findings
- Technical proof of concept, evidence and screenshots
- Remediation recommendations and conclusion
Each finding includes:
- Title and severity (Critical / High / Medium / Low / Informational)
- CVSS score and CWE reference
- Affected endpoint
- Description and business impact
- Reproduction steps and evidence
- Remediation advice
E. Free Retest (1x in 30 days)
After the report, request one retest within 30 days. Only previously reported findings are re-checked (not a new pentest). The report is updated with a status for each:
- Fixed
- Partially fixed
- Not fixed
- Unable to verify
F. Delivery Workflow
- 1. Onboarding: submit URL, application details and requirements
- 2. Authorization & scope: written authorization, in-scope assets, boundaries
- 3. Reconnaissance: map functionality, endpoints, auth flows, roles
- 4. Security assessment: manual + automated testing (OWASP Top 10)
- 5. Exploit validation: safe validation with evidence
- 6. Report preparation: severity, impact, reproduction, remediation
- 7. Delivery: secure report delivery, optional walkthrough
- 8. Retest: verify fixes once within 30 days
G. Package Limits & Exclusions
| Component | Limit |
|---|---|
| Target | 1 domain / web application |
| Testing | Manual + automated |
| Methodology | OWASP Top 10 |
| Reporting | 1 professional PDF report |
| Retest | 1 retest within 30 days |
| Support | Report clarification |
| Timeline | Within 5-7 days, depending on complexity |
⚠️ Exclusions
- Multiple websites or unrelated domains
- Unlimited subdomains or APIs
- Mobile application testing
- Source code review
- Cloud infrastructure penetration testing
- Social engineering
- Unlimited retesting
- Large enterprise applications without separate scoping
// IDEAL FOR
StartupsSaaS CompaniesSmall & Medium BusinessesWeb App OwnersE-commerce PlatformsDevelopers Preparing for Security Reviews
📸 // SAMPLE DELIVERABLE / TECHNICAL FINDING PREVIEW
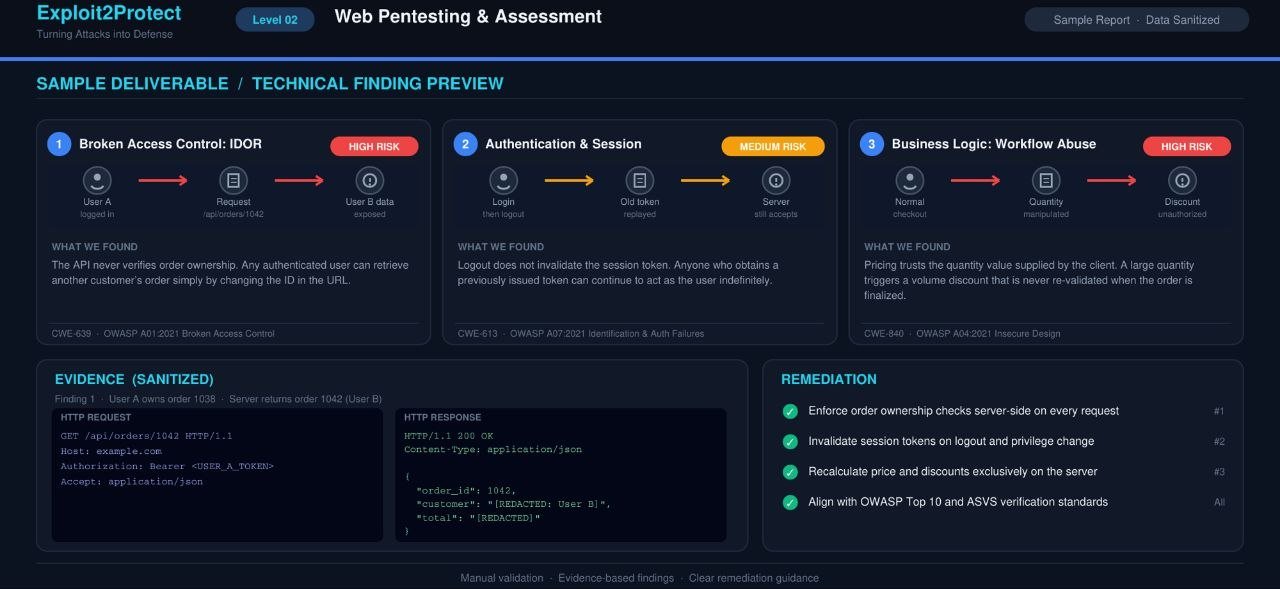
Real-world threat breakdown & clear remediation steps included in every assessment report.
// ORDER SERVICE OPTIONS
Written scope authorization and domain ownership confirmation are required before testing begins.
●SYSTEM READY // EXPLOIT2PROTECT SECURITY SERVICESSECURITY FIRST. ATTACK SMART. DEFEND BETTER.
E2P // SERVICE CATALOGUEREF ID: L03-PPT
LEVEL 03ADVANCED WEB + API7-15 DAYS DELIVERY
Professional Pentest
Advanced web application & API security assessment with verified attack chains.
PRICE
$500+ USD
// ASSESSMENT OBJECTIVE
Our flagship assessment goes beyond scanning and basic testing. We discover your attack surface, identify vulnerabilities, exploit them safely, investigate attack chains, and demonstrate the real business impact, with every finding verified manually.
// WHAT'S INCLUDED
🌐
Root Domain + Subdomains
Attack surface discovery & mapping
🔌
API Security Testing
REST, GraphQL, BOLA/IDOR, JWT
⛓️
Attack Chain Simulation
Multi-step exploitation & impact
🧪
Manual Exploit Verification
Safe, evidence-backed validation
📄
Full Technical Report
CVSS, CWE, diagrams, remediation
🔁
Free Retest
3x within 60 days
// TECHNICAL SCOPE & BREAKDOWN (tap to expand)
01. Attack Surface Assessment
- Root domain security assessment
- Subdomain discovery and validation
- Live host identification
- Technology fingerprinting
- Exposed services and administrative interfaces
- Staging and development environment exposure
- Sensitive information disclosure
- Attack surface mapping
Deliverable: Asset inventory and attack surface report.
02. API Security Assessment
- REST API security
- GraphQL security, if applicable
- BOLA / IDOR
- Broken Function Level Authorization
- Authentication bypass
- JWT and session security
- Mass assignment
- Sensitive data exposure
- Rate-limit weaknesses
- API business logic abuse
- Unauthorized workflow manipulation
Deliverable: API vulnerability findings with verified request/response evidence.
03. Advanced Attack Simulation
Our premium module: we go beyond single bugs and show how weaknesses combine into real attacks.
- Multi-step vulnerability investigation
- Authentication-to-authorization attack paths
- Privilege escalation chains
- API-to-web attack chains
- Information disclosure combinations
- Business logic exploitation
- Cross-account access scenarios
- Combined vulnerability impact analysis
Deliverable: Attack-chain diagrams, technical evidence, and business impact analysis.
04. Professional Reporting
- Executive summary
- Technical findings
- CVSS and CWE references
- Evidence and reproduction steps
- Attack-chain documentation
- Business risk analysis
- Remediation recommendations
Deliverable: Full technical penetration-testing report (PDF).
05. Remediation Verification
Free Retest: 3x within 60 days
- Round 01: initial remediation verification
- Round 02: verify remaining and revised fixes
- Round 03: final verification
Deliverable: Updated report and remediation status for each round.
06. Package Definition & Exclusions
| Feature | Professional Pentest |
|---|---|
| Root domain | 1 approved domain |
| Subdomains | Agreed in-scope assets |
| Web applications | Included within scope |
| APIs | Related approved APIs |
| User roles | Agreed test roles |
| Manual exploitation | Included |
| Attack chaining | Included |
| Technical report | Full PDF |
| Retesting | 3x / 60 days |
| Timeline | Estimated 7-15 business days |
⚠️ Exclusions
- Unlimited subdomains or API endpoints
- Multiple unrelated domains
- Mobile application testing
- Source code review
- Social engineering
- Unlimited retesting
- Very large or complex multi-role platforms (custom quotation)
// IDEAL FOR
SaaS PlatformsAPI-Driven BusinessesFinTech & E-commerceGrowing StartupsTeams Preparing for AuditsComplex Web Applications
// ORDER SERVICE OPTIONS
Written scope authorization and domain ownership confirmation are required before testing begins.
●SYSTEM READY // EXPLOIT2PROTECT SECURITY SERVICESSECURITY FIRST. ATTACK SMART. DEFEND BETTER.